Corp.DZ
A home lab that mirrors a small company network: Active Directory, Linux servers, group policy and security audits.
Brief
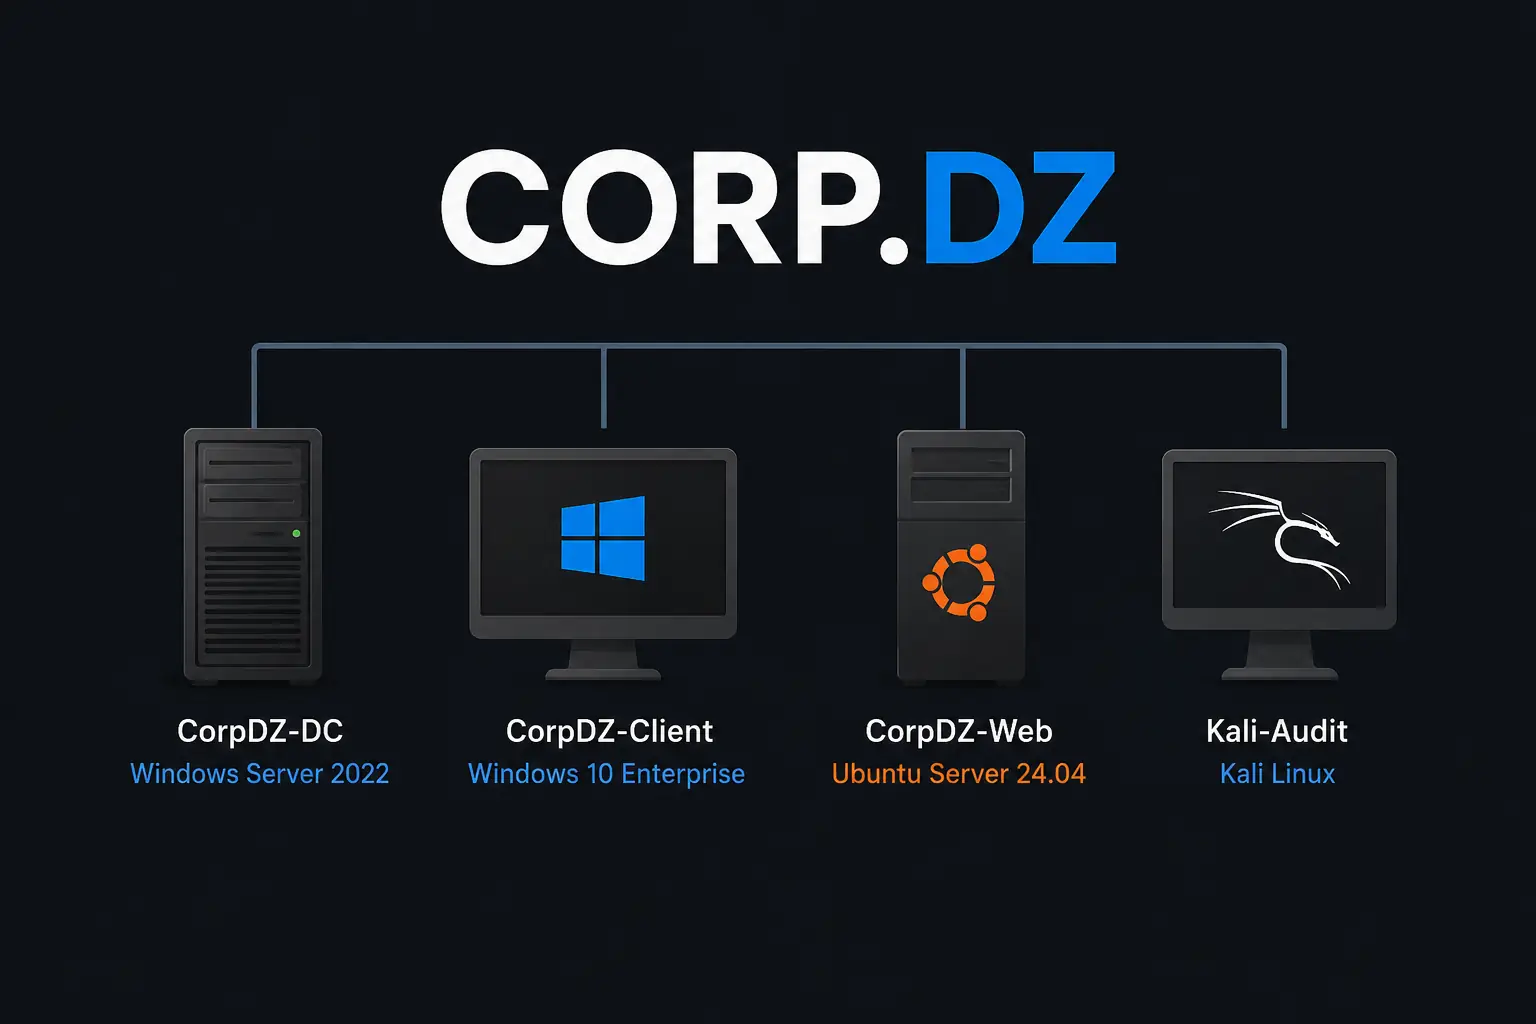
Corp.DZ is a hands‑on hybrid enterprise home lab engineered to emulate a Small‑to‑Medium Business (SMB) on‑premises network. The project models realistic corporate infrastructure using virtual machines in an isolated internal LAN. It integrates Windows Server Active Directory Domain Services with Linux-based intranet servers, automates administration tasks with PowerShell scripting, enforces organizational security policies via Group Policy Objects, and verifies vulnerabilities using defensive auditing techniques.
Screens
- Isolated Corporate LAN
- Built an air-gapped internal virtual network environment to safely test domain operations, service integrations, and security controls.
- Hybrid Active Directory Integration
- Connected Windows Server 2022 Domain Controller (corp.dz) with Ubuntu Server 24.04 hosting Nginx intranet web services.
- Automated User Provisioning
- Created custom PowerShell scripts to parse HR CSV files and programmatically provision Active Directory accounts with structured OUs.
- Group Policy Enforcement
- Configured GPOs to map network drives, set corporate wallpaper, enforce strict password policies, restrict account lockout limits, and deploy software via silent MSI installations.
- Active Security Auditing
- Performed defensive network reconnaissance and attack surface mapping from a Kali Linux instance using tools like nmap and netdiscover.
- Domain Configuration
- Promoted Windows Server 2022 to Domain Controller, configuring static DNS records, DHCP scope allocation, and loopback DNS resolution.
- Linux Intranet Web Server
- Configured static Netplan configuration on Ubuntu Server and created custom Windows DNS A records for cross-platform name resolution.
- Robust GPO Folder Redirection
- Implemented folder redirection to centralize user desktop directories using IP-hardcoded UNC paths (\\192.168.10.2\UserFiles\) to bypass boot-time DNS dependencies.
- PowerShell Automation Engine
- Built robust bulk user onboarding scripts using ConvertTo-SecureString for secure password generation and New-ADUser commands.
- Defensive Posture Verification
- Hardened default domain policies and simulated lockout scenarios to confirm security controls successfully mitigate threat profiles identified in scans.